inventory_routes.py | Lists routes and methods (Next.js, Express, Flask, FastAPI, Django, Laravel, Spring, ASP.NET, Rails, Go) and flags those with no evident authentication | Heuristic: does not prove that a control is correct or absent |
dynamic_authz_check.py | Tests access per identity | Localhost or an authorized host only; read-only by default; no response body stored |
prepass.py | Every tool in a fixed order, 14-area checklist pre-filled | Same output between runs; candidates are hypotheses |
merge_audits.py | Merges several runs on the same repo and measures agreement | A cause seen by one run only is not less true |
run_scanners.py | Dependencies from the lockfile alone and secrets in Git history, ranked without ever showing the value | Heuristic; if a scanner cannot run it says so |
import_openapi.py | Imports OpenAPI/Swagger and compares it with the routes in the code | The spec states intent, it does not prove protection |
iac_check.py | 14 rules on Docker, compose, Kubernetes, Terraform, GitHub Actions | Pattern-based hints, does not replace trivy/checkov |
import_scanner.py | Imports npm audit, SARIF, gitleaks, osv, semgrep, trivy, ZAP | Always hypotheses, severity never above "medium", secrets never reported |
verify_findings.py | Reviewer: nonexistent references, severity without evidence, duplicates; refutation brief for high findings | Mechanical: questions and refutation stay with the reader |
coverage_carry.py | Repeated audits: carries over coverage for unchanged content, marks changed items and never-covered files | The fingerprint proves the content did not change, not that the past review was right |
redact_check.py | Looks for secrets and personal data in files and PDFs | Never prints the value; a clean result is no guarantee |
cookie_scan.py | Cookies, storage and third parties before consent, clean browser | Local URLs or with the controller's confirmation |
draft_ropa.py | Draft Art. 30 register and supplier list from the code | All "hypotheses": roles and legal bases are confirmed by the controller |
draft_dpia.py | Draft DPIA sheet (Art. 35) from the processing map, with need indicators | Not a DPIA and does not decide whether one is needed: the controller decides with the DPO |
retention_check.py | Deletion evidence compared with declared retention times | Absence of evidence is not a violation |
check_delivery.py | A single check before delivery: schema, refutations of high findings, GDPR matrix, redaction (including the app's secret values), forbidden words, coverage | Mechanical: a clean result does not prove the audit is correct; it cannot see chat messages |
canonicalize.py | Converts English states and severities to the canonical Italian values the scripts check | Touches only enumerated values, never free text |
compare_audits.py, export_findings.py | Retest between two audits; CSV, SARIF, Markdown | "Resolved" means absent, not verified |
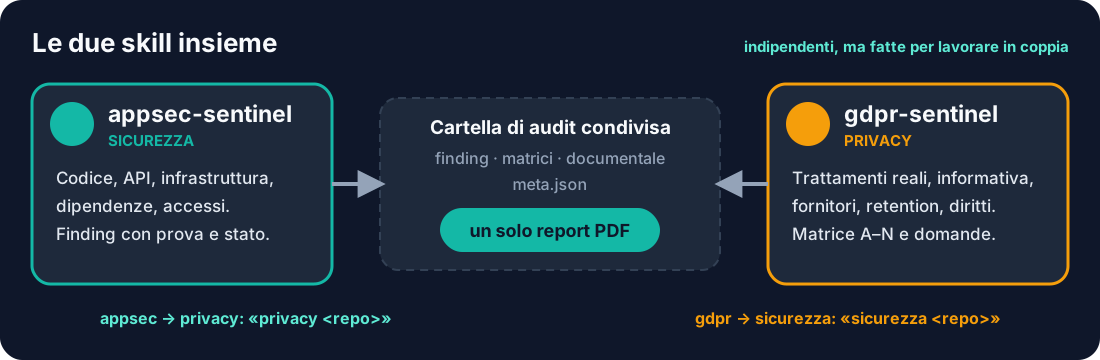
build_report_pdf.py | PDF report: full, --sintetico, --lang en, --previous, --nis2 | The NIS2 mapping is indicative, not a compliance assessment |